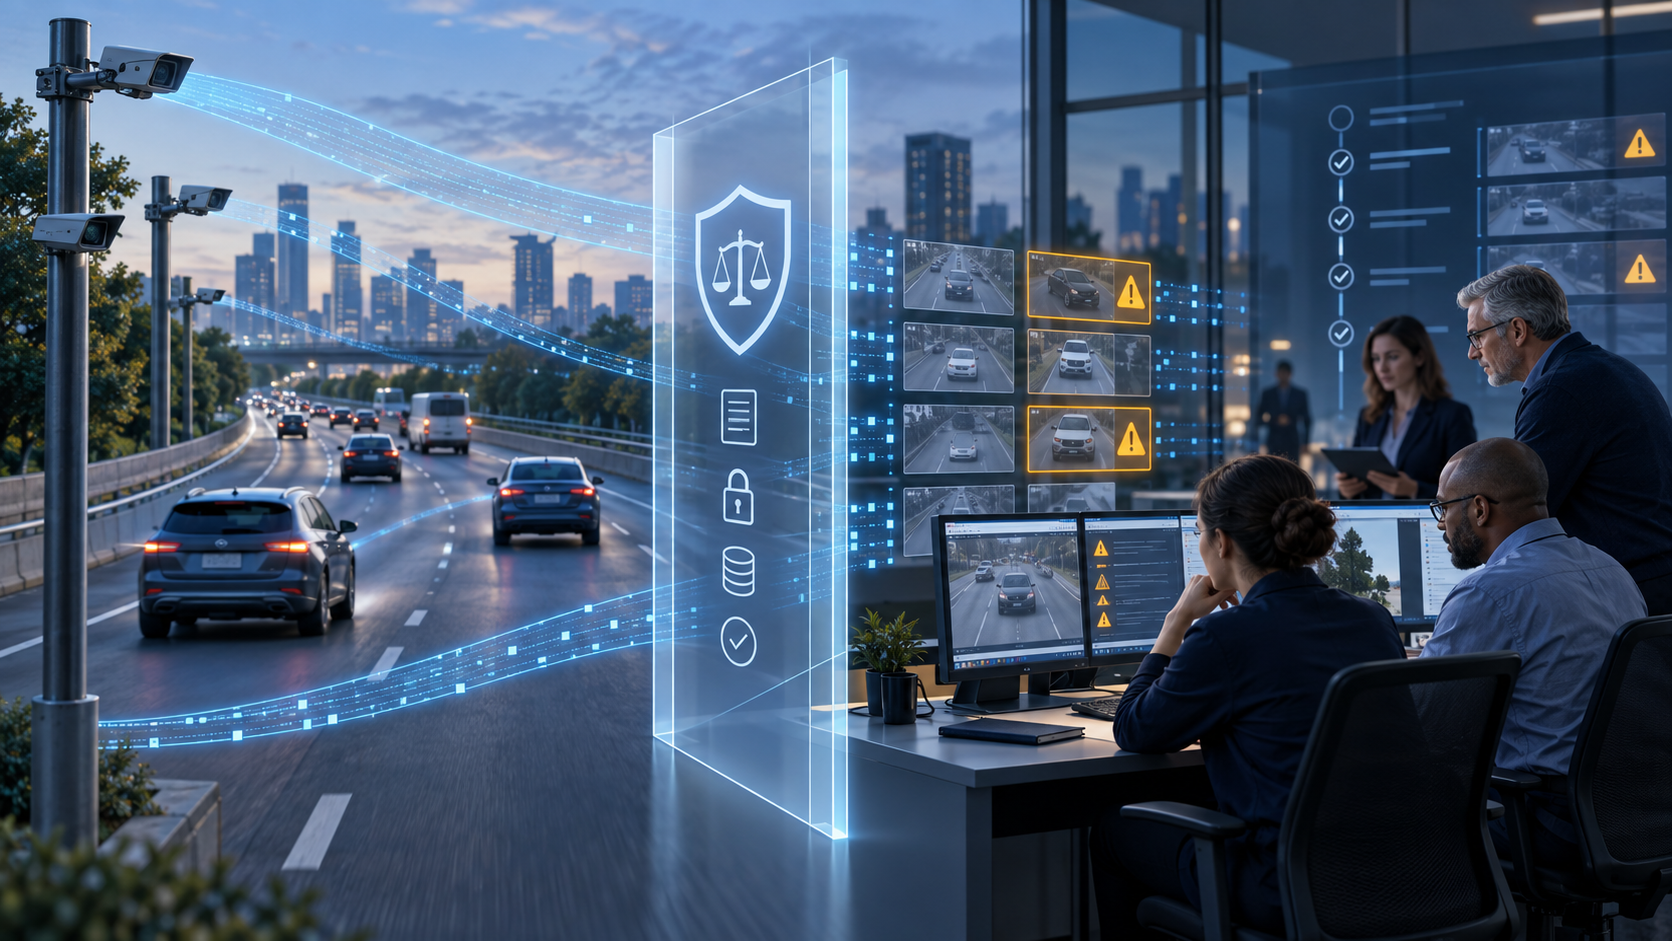
The latest stories about Flock Safety cameras are disturbing.
Police officers have been accused of using license-plate searches to track former partners, relatives, and other people for reasons unrelated to legitimate police work. A Washington Post investigation identified at least 69 police officials accused, charged, or convicted of misusing Flock or other license-plate-reader systems. In at least 15 of those cases, someone outside the department found the potential misuse first. One department reportedly went nearly two years without auditing searches while an officer repeatedly searched for his wife's vehicle. (https://www.washingtonpost.com/technology/2026/08/19/we-found-cops-who-misused-flock-their-police-departments-didnt-know/)
Another review found officers entering reasons such as "LMAO," "IDK," and keyboard nonsense before searching a system capable of following a vehicle across thousands of cameras and jurisdictions. Those examples came from records covering 2023 through late 2025. They show that requiring someone to type something into a box is not the same as requiring justification. (https://www.404media.co/cops-search-thousands-of-flock-cameras-for-reasons-of-lmao-idk-hehe-and-asdfg/)
The instinctive response is understandable: the technology is dangerous, so get rid of the technology.
I think that conclusion is incomplete.
The camera did not decide to stalk an ex-partner. An algorithm did not decide that "LMAO" was a legitimate investigative purpose. A person used authority and access in a way that should never have been permitted... and the organization responsible for that authority often failed to notice.
That is a human-governance failure, amplified by technology.
We should not excuse the design
Saying that people misused the system does not absolve the system's designers, its vendor, or the agencies that deployed it.
Technology changes the scale of what one person can do. A dishonest employee once had to follow someone physically, recruit help, or search several disconnected systems. A broadly connected license-plate network can compress that effort into a few keystrokes. Poor design can turn an individual abuse of authority into fast, inexpensive, interstate surveillance.
Boston's experience shows why the problem is larger than a few improper searches. During a 2025 pilot, Boston officials discovered that vehicle data was being distributed to outside law-enforcement agencies even though the agreement said sharing would be disabled. The city identified the problem three days into the pilot and ordered the setting changed. (https://www.wbur.org/news/2026/09/14/flock-boston-police-pilot-surveillance-technology-report)
That was not an officer stalking someone. It was a control failure between contractual intent, system configuration, vendor behavior, and verification.
The honest position has to hold both truths at once:
- People remain accountable for how they use authority.
- Vendors and deploying organizations remain accountable for making abuse difficult, visible, and consequential.
Blaming "AI" for every abuse lets the responsible human disappear into the machinery. Blaming only a rogue user lets weak architecture and negligent oversight disappear with them.
1984 was not a warning about a television screen
When people compare modern surveillance to 1984, they sometimes talk as if the technology itself became the dictator.
It did not.
The horror was organized power using surveillance, secrecy, fear, and information control without meaningful limits or recourse. The telescreen mattered because an unaccountable authority controlled it.
That distinction matters now. Removing every AI-assisted tool would not remove the human appetite to misuse authority. History has no shortage of surveillance, intimidation, selective enforcement, and records abuse from long before machine learning.
AI did not invent the bad actor. It gave the bad actor reach.
So the responsible response cannot be blind adoption... but it also cannot be pretending that refusing modern tools will make abusive people disappear. The better response is to use modern controls to make abuse harder to hide than it was in the manual world.
Use AI to audit the humans using AI
Every consequential search should produce evidence:
- Who performed it?
- What case or authorized purpose supported it?
- Which data and jurisdictions were searched?
- What result was viewed, exported, or shared?
- Was the search performed during an assigned investigation?
- Did the same user repeatedly search for the same person, vehicle, address, or relationship?
- Was an emergency exception used, and was it reviewed afterward?
- Did the user change search language after a warning or denial?
A human supervisor can review a few records. A large agency or regional network may generate far more activity than a person can evaluate consistently. That is an appropriate place for applied AI.
An auditing model can look for unusual repetition, searches disconnected from assigned cases, access outside normal duties, vague or fabricated reasons, repeated emergency overrides, queries involving known personal relationships, unusual cross-jurisdiction activity, and attempts to work around policy controls. It can rank the events that deserve immediate review without declaring anyone guilty.
That distinction is critical. The audit model should identify risk. An independent, accountable person should investigate the context and decide what it means.
South Portland used AI-assisted analysis while reviewing a large set of Flock network audit records covering February 2025 through May 2026. That does not prove AI auditing is sufficient, but it demonstrates the practical point: AI can help people examine activity at a scale that manual review may not handle well. The city ultimately ceased its use of Flock and stopped sharing data with other agencies after public review. (https://www.southportland.org/DocumentCenter/View/4636/June-11-2026-Update_-City-of-South-Portland-Completes-Review-of-Flock-Datadocx) (https://southportland.gov/m/newsflash/home/detail/550)
Flock has announced that it will require its Audit Assistance feature for law-enforcement customers, require case codes, flag emergency bypasses, introduce proactive lockouts, and recommend a seven-day default retention period. Those are meaningful changes. They are also controls announced after misuse exposed why optional oversight was inadequate. (https://www.flocksafety.com/blog/flock-guardrails-address-lpr-privacy-concerns-and-police-transparency)
The lesson is not that an AI auditor will solve the problem. The lesson is that a powerful AI-enabled system should never depend on someone occasionally remembering to inspect a spreadsheet.
The watchdog needs guardrails too
"Use AI to police the people policing people with AI" sounds circular... and it becomes dangerous if the second system simply creates more surveillance.
The audit layer needs a narrow purpose and a different authority boundary.
It should analyze access behavior and policy compliance, not build a second unlimited location database. It should use the minimum evidence needed to identify suspicious use. Its rules, alerts, overrides, and false positives should be reviewable. Administrators should not be able to quietly erase an alert concerning themselves. The people operating the original system should not be the only people judging whether they used it properly.
I would expect, at minimum:
- Named access, never shared credentials. Every action must belong to an identifiable user.
- Case-linked authorization before the search. A reason field is not enough. The case must exist, the user must be assigned or specifically authorized, and the scope must match the purpose.
- Immutable logs. Search, export, sharing, configuration, warning, override, and deletion activity must be reconstructable.
- Automated anomaly detection. Repeated targets, unusual hours, personal associations, cross-agency patterns, vague justifications, and emergency bypasses should generate reviewable alerts.
- Independent review. High-risk alerts should reach an inspector general, civilian oversight body, internal-affairs function with genuine independence, or another authority outside the operator's normal chain.
- Real consequences. A control without a defined response is a suggestion. Access suspension, investigation, disclosure requirements, and disciplinary paths need to exist before an incident.
- Public aggregate reporting. Communities should be able to see search volumes, rejected searches, overrides, sharing relationships, audit frequency, confirmed misuse, and corrective action without exposing active investigations.
- Short retention and evidence-specific preservation. Keeping everything because it may someday become useful is not governance.
- A tested shutdown path. If the controls fail, the organization must be able to suspend searches or sharing without waiting for a vendor or a news investigation.
- Regular adversarial testing. The organization should test whether a determined insider can misuse the system, conceal a search, abuse an exception, or exploit another agency's access.
NIST's AI Risk Management Framework points in the same direction: instrument systems for measurement, retain histories and audit logs, document human oversight, track exceptions and escalations, and evaluate whether accountability mechanisms actually work. (https://airc.nist.gov/docs/AI_RMF_Playbook.pdf)
This is bigger than Flock
The same pattern appears anywhere AI expands what one authorized person can do.
An employee can use an AI assistant to summarize records they were never supposed to collect. A developer can give an agent production access because the manual process feels slow. A manager can use generated analysis to justify a decision without checking the evidence. A security team can deploy monitoring that becomes employee surveillance. A customer-service platform can combine data across boundaries that existed for good reasons.
The AI is part of the risk, but governance determines whether one questionable action becomes an alert, a preventable incident, or an invisible habit.
This is why I resist arguments that end with "ban the AI" or "trust the human."
Humans need tools. Humans also need boundaries. The more capable the tool becomes, the less an organization can rely on personal integrity as its only control.
I am not asking anyone to trust Flock, a police department, an AI vendor, or an audit model because it says the right words. Trust should follow evidence.
Show me that access is limited before it is used. Show me that every consequential action is attributable. Show me that abnormal behavior is surfaced quickly. Show me that the reviewer is independent. Show me that misuse carries consequences. Show me that the public can verify the system is operating within the authority it was given.
The question is not whether AI is good or bad.
The question is whether we will use it to concentrate unaccountable power... or to make the exercise of power more visible, constrained, and answerable to the people affected by it.
AI has made surveillance more powerful.
Applied responsibly, it can also make abuse much harder to hide.